Feature #8812
closedAdd "Select All" to Firewall/NAT rule lists
100%
Description
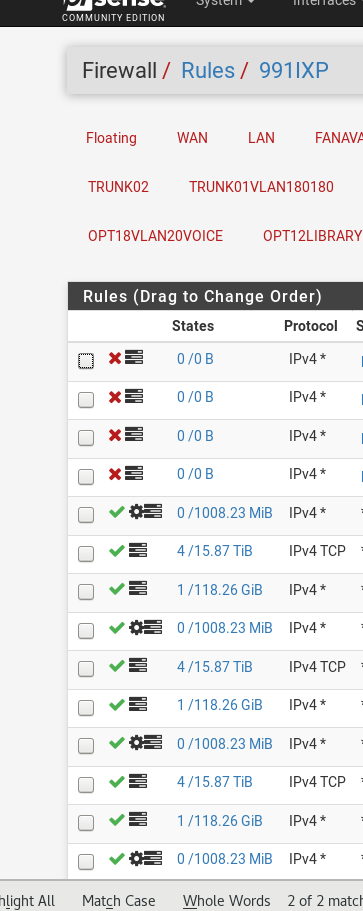
pfSense does not have select all (Firewall -> Rules).
cannot select all rows in firewall rules.
imagine firewall rule has 1000 row and want select all or reverse select.
Files
JP Updated by Jim Pingle about 8 years ago
- Tracker changed from Bug to Feature
- Subject changed from pfsense has forgotten the select all to Add "Select All" to Firewall/NAT rule lists
- Description updated (diff)
- Category set to Rules / NAT
- Target version set to Future
Not a bug, but a feature request. That page has not had a select all mechanism that I could see. Checked back to 2.1.
 Updated by Anonymous about 8 years ago
- Status changed from New to Feedback
- Assignee set to Anonymous
Updated by Anonymous about 8 years ago
- Target version changed from Future to 2.4.4
Updated by Anonymous about 8 years ago
- % Done changed from 0 to 100
Applied in changeset commit:e969408dc18a109c224da3feef4bcc69626f25dd.
CK Updated by Constantine Kormashev about 8 years ago
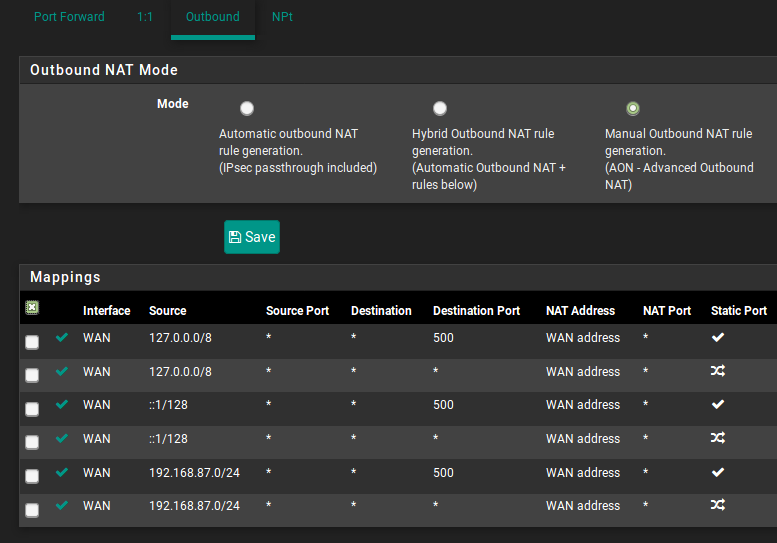
New feature works fine for:firewall_nat.phpfirewall_rules.php
But does not exist for:firewall_nat_1to1.phpfirewall_nat_out.phpfirewall_nat_npt.php
CK Updated by Constantine Kormashev about 8 years ago
- Status changed from Feedback to Assigned
Updated by Anonymous about 8 years ago
- Status changed from Assigned to Feedback
Control has been added to all NAT pages
SW Updated by Steve Wheeler about 8 years ago
- File Selection_476.png Selection_476.png added
The control is now present on NAT rules but does not seem to actually function. Clicking 'select all' does not select anything. See screenshot:
Tested in:
2.4.4-DEVELOPMENT (amd64)
built on Fri Aug 24 16:24:53 EDT 2018
FreeBSD 11.2-RELEASE-p2
SW Updated by Steve Wheeler about 8 years ago
- Status changed from Feedback to Assigned
Updated by Anonymous about 8 years ago
- Status changed from Assigned to Feedback
Rule table given ID so selectall control can find it
Updated by Anonymous about 8 years ago
Select all works as expected on Firewall > NAT > Port Forward/1:1/Outbound/NPt and at Firewall > Rules on 2.4.4.a.20180824.1144 (gitsync'd to master).
Updated by Anonymous about 8 years ago
- Status changed from Feedback to Resolved