Actions
Regression #14678
closed
JP
JP
CA and Certificate renewal page does not properly list some SHA1 certificates as being weak
Regression #14678:
CA and Certificate renewal page does not properly list some SHA1 certificates as being weak
Start date:
Due date:
% Done:
100%
Estimated time:
Plus Target Version:
23.09
Release Notes:
Default
Affected Version:
2.7.0
Affected Architecture:
Description
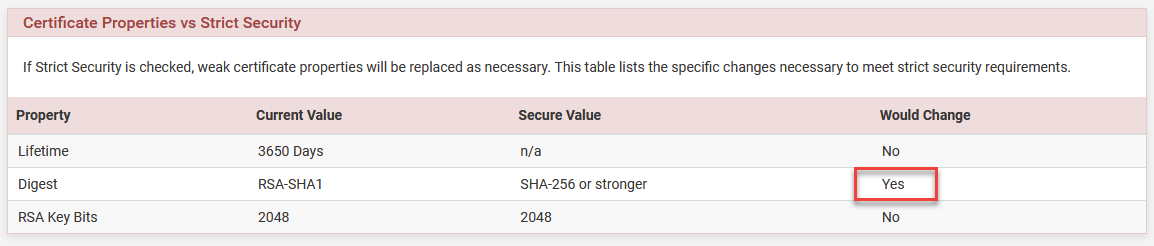
Noticed this when working on other OpenSSL changes, but some certificates are not being flagged by the renewal page as being weak. The "Would change" column says "No" when it should say "Yes". The most obvious example here is one with a digest listed as "RSA-SHA1". It's being converted to lowercase but the list it's being checked against is mixed case.
This can also affect the renewal process.
I'm fixing this along with other changes for #14672 and #14677
Files


Actions