Feature #16444
closedUpdating unbound (DNS resolver) configuration option to relfect RFC 8767 changes upstream.
0%
Description
I helped contribute code some yeaars back to add serve-expired support to Unbound in pfSense, this grants more performant DNS queries for anything that has been cached since the last unbound restart.
Since the release of Unbound 1.23.0 the default behaviour of serve expired if enabled has been changed to reflect RFC8767, it is now used as a serve stale record, so only uses expired cache when a upstream resolver doesnt respond within 1800ms.
I have created a patch which will make this more than just a on/off switch, the options change to off (default as is now), serve expire (the old behaviour), and serve stale (the new RFC 8767 behaviour).
Unbound was updated to 1.23.0 in pfSense 2.8.1, and I assume its at least this new in the latest plus build.
Info here.
https://nlnetlabs.nl/news/2025/Apr/24/unbound-1.23.0-released/
I will provide two patches, one that does work in the current build of 2.8.1 but I think wont apply cleanly to dev code, and another patch might apply cleanly to dev code that takes into account another recent patch made.
The patch when active on the old behaviour option adds a new config variable line.
serve-expired-client-timeout: 0
When set to off or RFC8767 the line isnt added at all, its designed this way so user's still have a way of configuring a customised 'serve-expired-client-timeout' in the custom box in the GUI. Also it will also not need patching again if for some reason the default value of this changes again in a newer Upbound version. This method would just inherit the new default.
I also checked the behaviour of how it behaves when patch is applied and serve-expired is currently enabled, it will correctly keep it enabled. I have managed to with this patch avoid using an extra configuration which would have added more clutter to the advanced page.
Of course the patch can be tweaked, in case Netgate want to change the wording.
Files
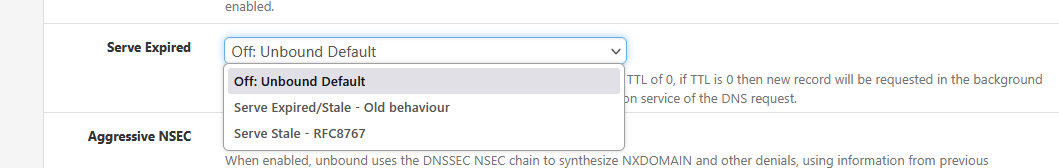
CC Updated by Chris Collins 12 months ago
Attaching screenshot of change,
CC Updated by Chris Collins 4 days ago
Hi, if you wish to reject this patch (which wouldnt have changed the default), you still need to patch, as the current description for the feature is now misleading.
The new default behaviour is still to have no serve expired at all.
The new sub default if serve expired is enabled, is effectively a serve stale. (this happens now if serve expired is enabled in unbound, the description still states the old behaviour).
The original spirit of the option is no longer there if this proposal is rejected, so you should probably change the description to explain it only will cache an expired response if the upstream times out and its no longer a performance tweak, and maybe add in the description, the value to add to custom, if the user wants the old behaviour back.
I have just been dealing with someone on reddit, who suffered a large DNS regression due to the loss of serve-expire in pfSense after updating.