Bug #11548
closed"rule expands to no valid combination" error from port forward automatic rule mixing IPv4 and IPv6 elements
0%
Description
After a upgrade from 2.4.5 (pfsense FE) to 21.02 (the new pfsense+), the router (Netgate SG-4860) goes on all networks in DEFAULT DENY ALL and ignores all the configured firewall rules.
- I had to connect to the console and disable the firewall via pfctl d After trying to connect to the gui on the configured network, it did not work and I had to visit the gui via the LAN network.
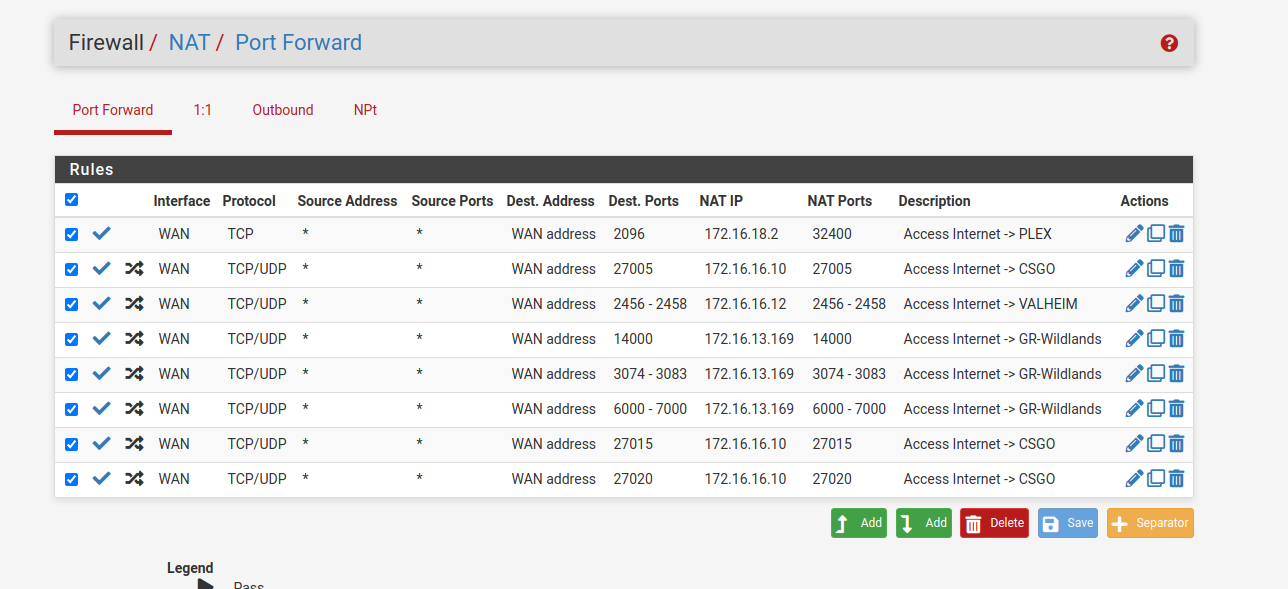
- The following messages popped up on the gui, it appears to be that after the upgrade, pfsense cannot read 1 NAT rule due to a parsing error:
There were error(s) loading the rules: /tmp/rules.debug:245: rule expands to no valid combination - The line in question reads [245]: pass in log quick on $WAN reply-to ( igb1 <ipv6_ip> ) inet6 proto { tcp udp } from any to <ipv4_ip> port 2455 >< 2459 tracker 1613566521 keep state label "USER_RULE: NAT Access Internet -> VALHEIM" @ 2021-02-20 22:58:49
- I removed the conflicting line in question and everything worked again.
I think it had something to do with the port range being specified in the NAT rule, because I had several others configured but this was the only one that was giving issues.
Files