Actions
Bug #7356
closed
AW
JP
pfsense 2.3.4: TCP State Timeout cannot be higher than 3600s within a rule - global configuration allows higher values
Bug #7356:
pfsense 2.3.4: TCP State Timeout cannot be higher than 3600s within a rule - global configuration allows higher values
Start date:
03/06/2017
Due date:
% Done:
100%
Estimated time:
Plus Target Version:
Release Notes:
Affected Version:
All
Affected Architecture:
All
Description
Hi,
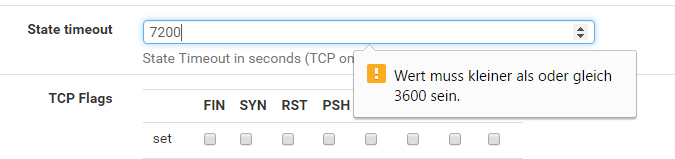
whe I am within a firewall rule and change the "TCP State Timeout" under "Advaced options" within that specific rule I cannot set the value higher than 3600s.
Under System --> Advanced --> Firewall & NAT I can configure higher values and the default values are higher than 3600s.
So I would assume it should be possible to set any timeout possible individually on each firewall rule.
Files
JP Updated by Jim Pingle over 9 years ago
- Category set to Rules / NAT
- Status changed from New to Confirmed
- Assignee set to Jim Pingle
- Target version set to 2.3.3-p1
- Affected Version changed from 2.3.3 to All
- Affected Architecture All added
- Affected Architecture deleted (
)
You're right, that should not be limited in that way.
It affects 2.4 as well.
Easy fix, I'll push it momentarily.
JP Updated by Jim Pingle over 9 years ago
- Status changed from Confirmed to Feedback
- % Done changed from 0 to 100
Applied in changeset commit:12210bd40d60757e09e09f433f7ce5536f686c97.
RB Updated by Renato Botelho over 9 years ago
- Status changed from Feedback to Resolved
Works
Actions