Bug #12076
closedOpenVPN RADIUS-based firewall rules do not use expected value for RADIUS-assigned IP addresses
0%
Description
Current OpenVPN script implemented to trigger Cisco-AVPair ACL in PF chains allows the {clientip} syntax to match IP address of the client initiating the VPN connection.
The script (/usr/local/sbin/openvpn.attributes.sh) relies on ${ifconfig_pool_remote_ip} variable passed from OpenVPN to generate a PF rule (temporary file) to later insert in PF running configuration.
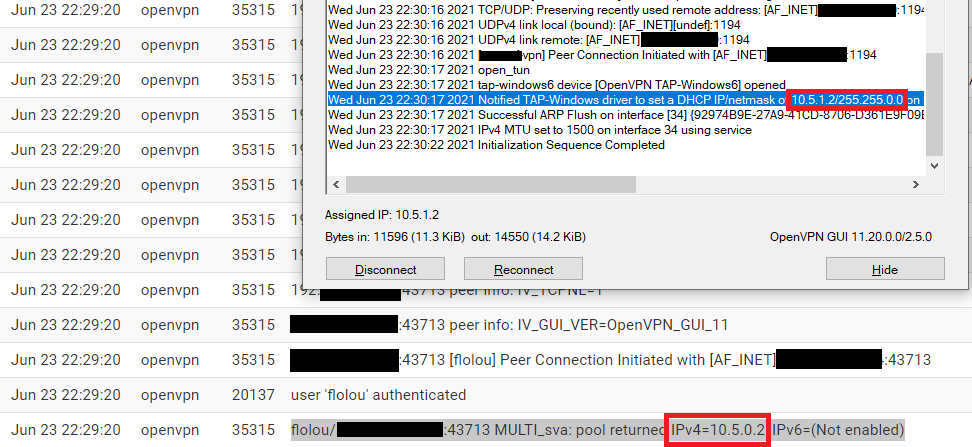
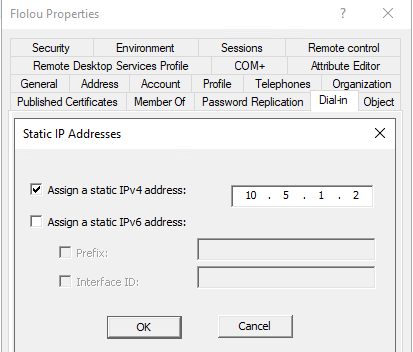
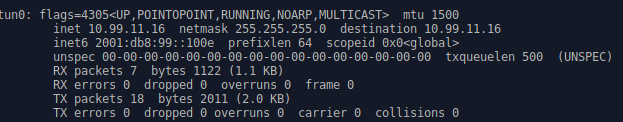
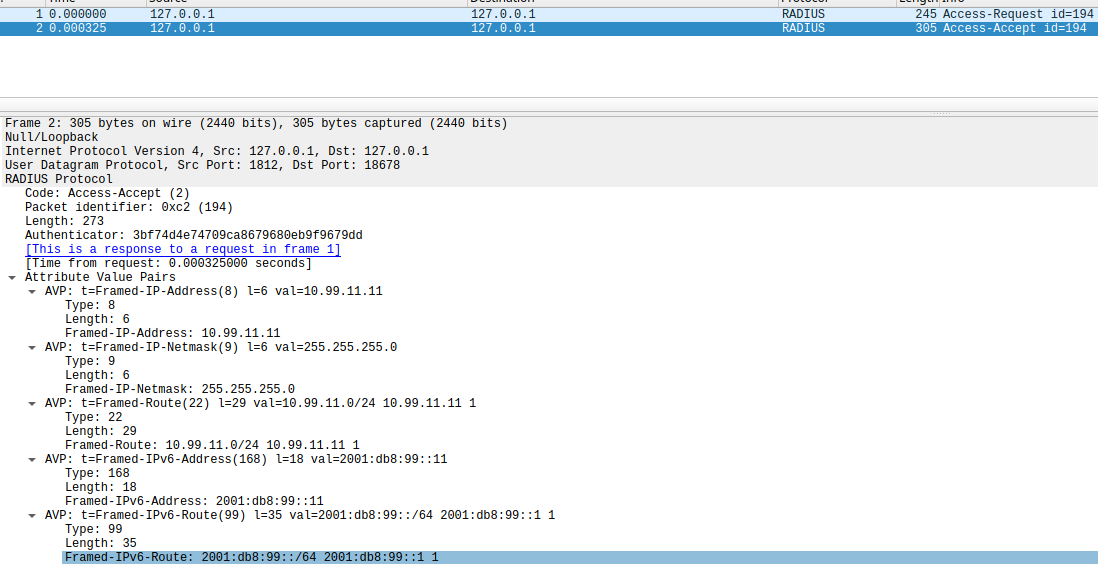
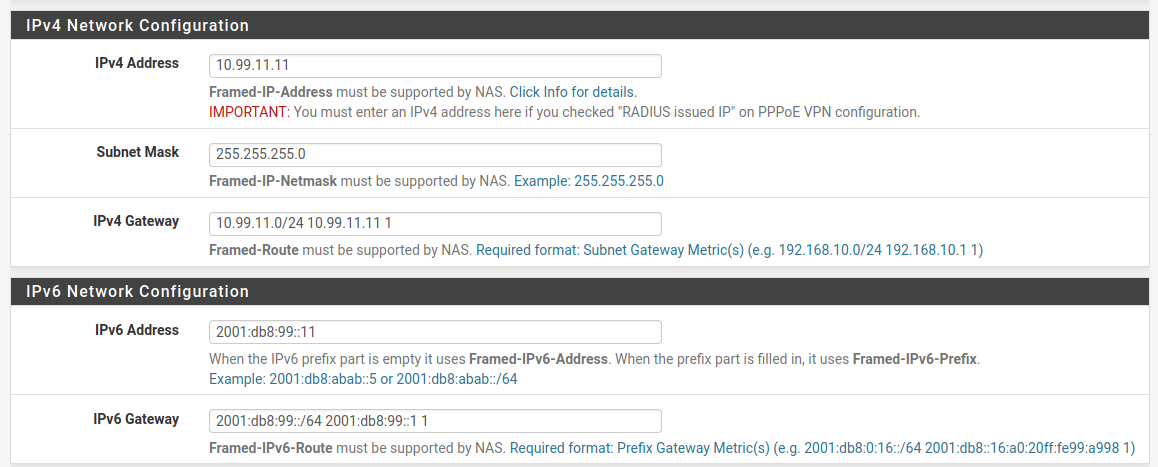
For some reason the IP address returned by the OpenVPN pool is not the same as the Framed-IP-Address indicated by Radius (see screenshots). I also dumped variables passed by OpenVPN to the script and none contains the Framed-IP-Address.
The workaround I implemented on my pfsense was to replace the {clientip} substitution pattern while processing /etc/inc/util.inc if a framed_ip is set in attribute.
Files