Actions
Regression #13628
closed
GP
MM
pfSense - Feature #13446: Upgrade PHP from 7.4 to 8.1
FreeRADIUS Users cleared out each time a user is add, removed, or modified
Regression #13628:
FreeRADIUS Users cleared out each time a user is add, removed, or modified
Start date:
Due date:
% Done:
100%
Estimated time:
Plus Target Version:
23.01
Affected Version:
2.7.0
Affected Plus Version:
23.01
Affected Architecture:
All
Description
After upgrading from Stable to Development I noticed that my RADIUS authentication was broken. I'm using a very basic setup with users being stored locally in a file and PAP; no SQL, LDAP, or VPN. The only complication is that I have a few VLANs.
I troubleshooted the problem for a while and found the following:
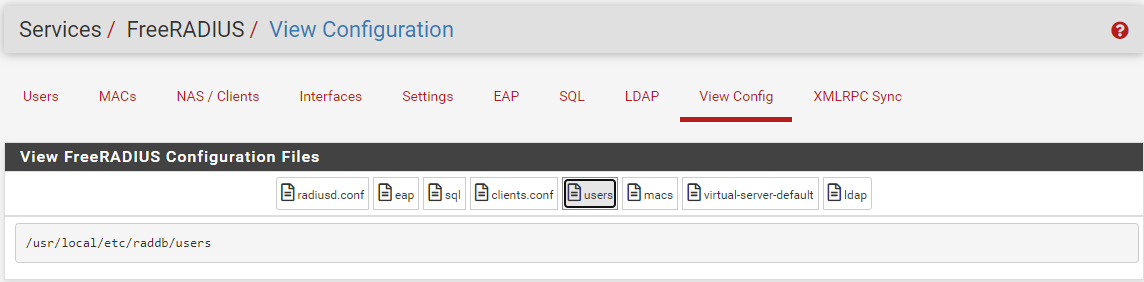
- Each time a user is added, removed, or modified via Services > FreeRADIUS > Users , the
/usr/local/etc/raddb/mods-config/files/authorizefile is cleared and not repopulated - When a user is attempting a login, radiusd cannot find the last good known password, because there are no users in the local database; it doesn't set
Auth-Type, and the login fails in post-auth - Naturally, tests via Diagnostics > Authentication also fail, and pfSense web admin logins fail and fall back to the local database
- If I manually add the user to the local database file, authentication works fine like before
- Simply stopping and restarting the services via GUI or console does not clear the user database
I'm not familiar with how the GUI wrapper in pfSense works, but it seems to me that the user configuration is no longer written correctly.
My server is on:
2.7.0-DEVELOPMENT (amd64)
built on Thu Nov 03 06:04:43 UTC 2022
FreeBSD 14.0-CURRENT
Files

Actions